Substack now has a TV app

It was only 16 months ago that Substack expanded into live video. Since then, it's become a widely adopted medium on the platform, including by its ever-growing list of cable news expats. Now, the company has decided it's ready for a bigger screen. Starting today, you can install a new Substack TV app on Apple TV and Google TV devices.

Substack describes the app's initial launch as focusing on "reliable, high-quality viewing" for the platform's long-form videos. It centers around video posts and livestreams from the creators and publications you follow. There's also a "For You" section that combines those videos with algorithmic recommendations. And you can browse dedicated pages for each channel.

Viewing access aligns with your subscription level. So, if a channel restricts videos to paying subscribers on Substack’s mobile app and website, the same paywall applies here. However, the company says it's working on adding previews of paid content for free subscribers. It also plans to add audio posts, search, improved discovery and separate sections for different shows within a single publication.

At least one of those legacy media expats who moved to Substack is optimistic about the feature. "This is a game-changing moment for the rise of independent media," former CNN anchor Jim Acosta wrote in the announcement post. "Substack has proven that legacy media consumers are not only searching for fresh alternatives; they are finding them."

Based on the comments in Substack’s announcement, some of the platform’s die-hards are less enthusiastic than Acosta. “File this under – thing we didn’t ask for,” Ashli Pollard wrote. “This is not YouTube,” a commenter named Dustin added. “Elevate the written word.” I personally don’t see any harm in another way to watch the videos Substack already hosts. (Its newsletters aren’t going anywhere.) But given how Big Tech companies tend to pivot further toward the most en vogue (and profitable) medium of the day, I can see why purists feel the need to dig in their heels.

Regardless, you can find the Substack TV app by searching for its name in the tvOS App Store or the Apps section on Google and Android TV devices. You can sign in by scanning a QR code with your phone.

This article originally appeared on Engadget at https://www.engadget.com/entertainment/streaming/substack-now-has-a-tv-app-195408592.html?src=rss

Grok generated an estimated 3 million sexualized images — including 23,000 of children — over 11 days

We already knew xAI's Grok was barraging X with nonconsensual sexual images of real people. But now there are some numbers to put things in perspective. Over an 11-day period, Grok generated an estimated 3 million sexualized images — including an estimated 23,000 of children.

Put another way, Grok generated an estimated 190 sexualized images per minute during that 11-day period. Among those, it made a sexualized image of children once every 41 seconds.

On Thursday, the Center for Countering Digital Hate (CCDH) published its findings. The British nonprofit based its findings on a random sample of 20,000 Grok images from December 29 to January 9. The CCDH then extrapolated a broader estimate based on the 4.6 million images Grok generated during that period.

The research defined sexualized images as those with "photorealistic depictions of a person in sexual positions, angles, or situations; a person in underwear, swimwear or similarly revealing clothing; or imagery depicting sexual fluids." The CCDH didn't take image prompts into account, so the estimate doesn't differentiate between nonconsensual sexualized versions of real photos and those generated exclusively from a text prompt.

The CCDH used an AI tool to identify the proportion of the sampled images that were sexualized. That may warrant some degree of caution in the findings. However, I'm told that many third-party analytics services for X have reliable data because they use the platform's API.

On January 9, xAI restricted Grok's ability to edit existing images to paid users. (That didn't solve the problem; it merely turned it into a premium feature.) Five days later, X restricted Grok's ability to digitally undress real people.

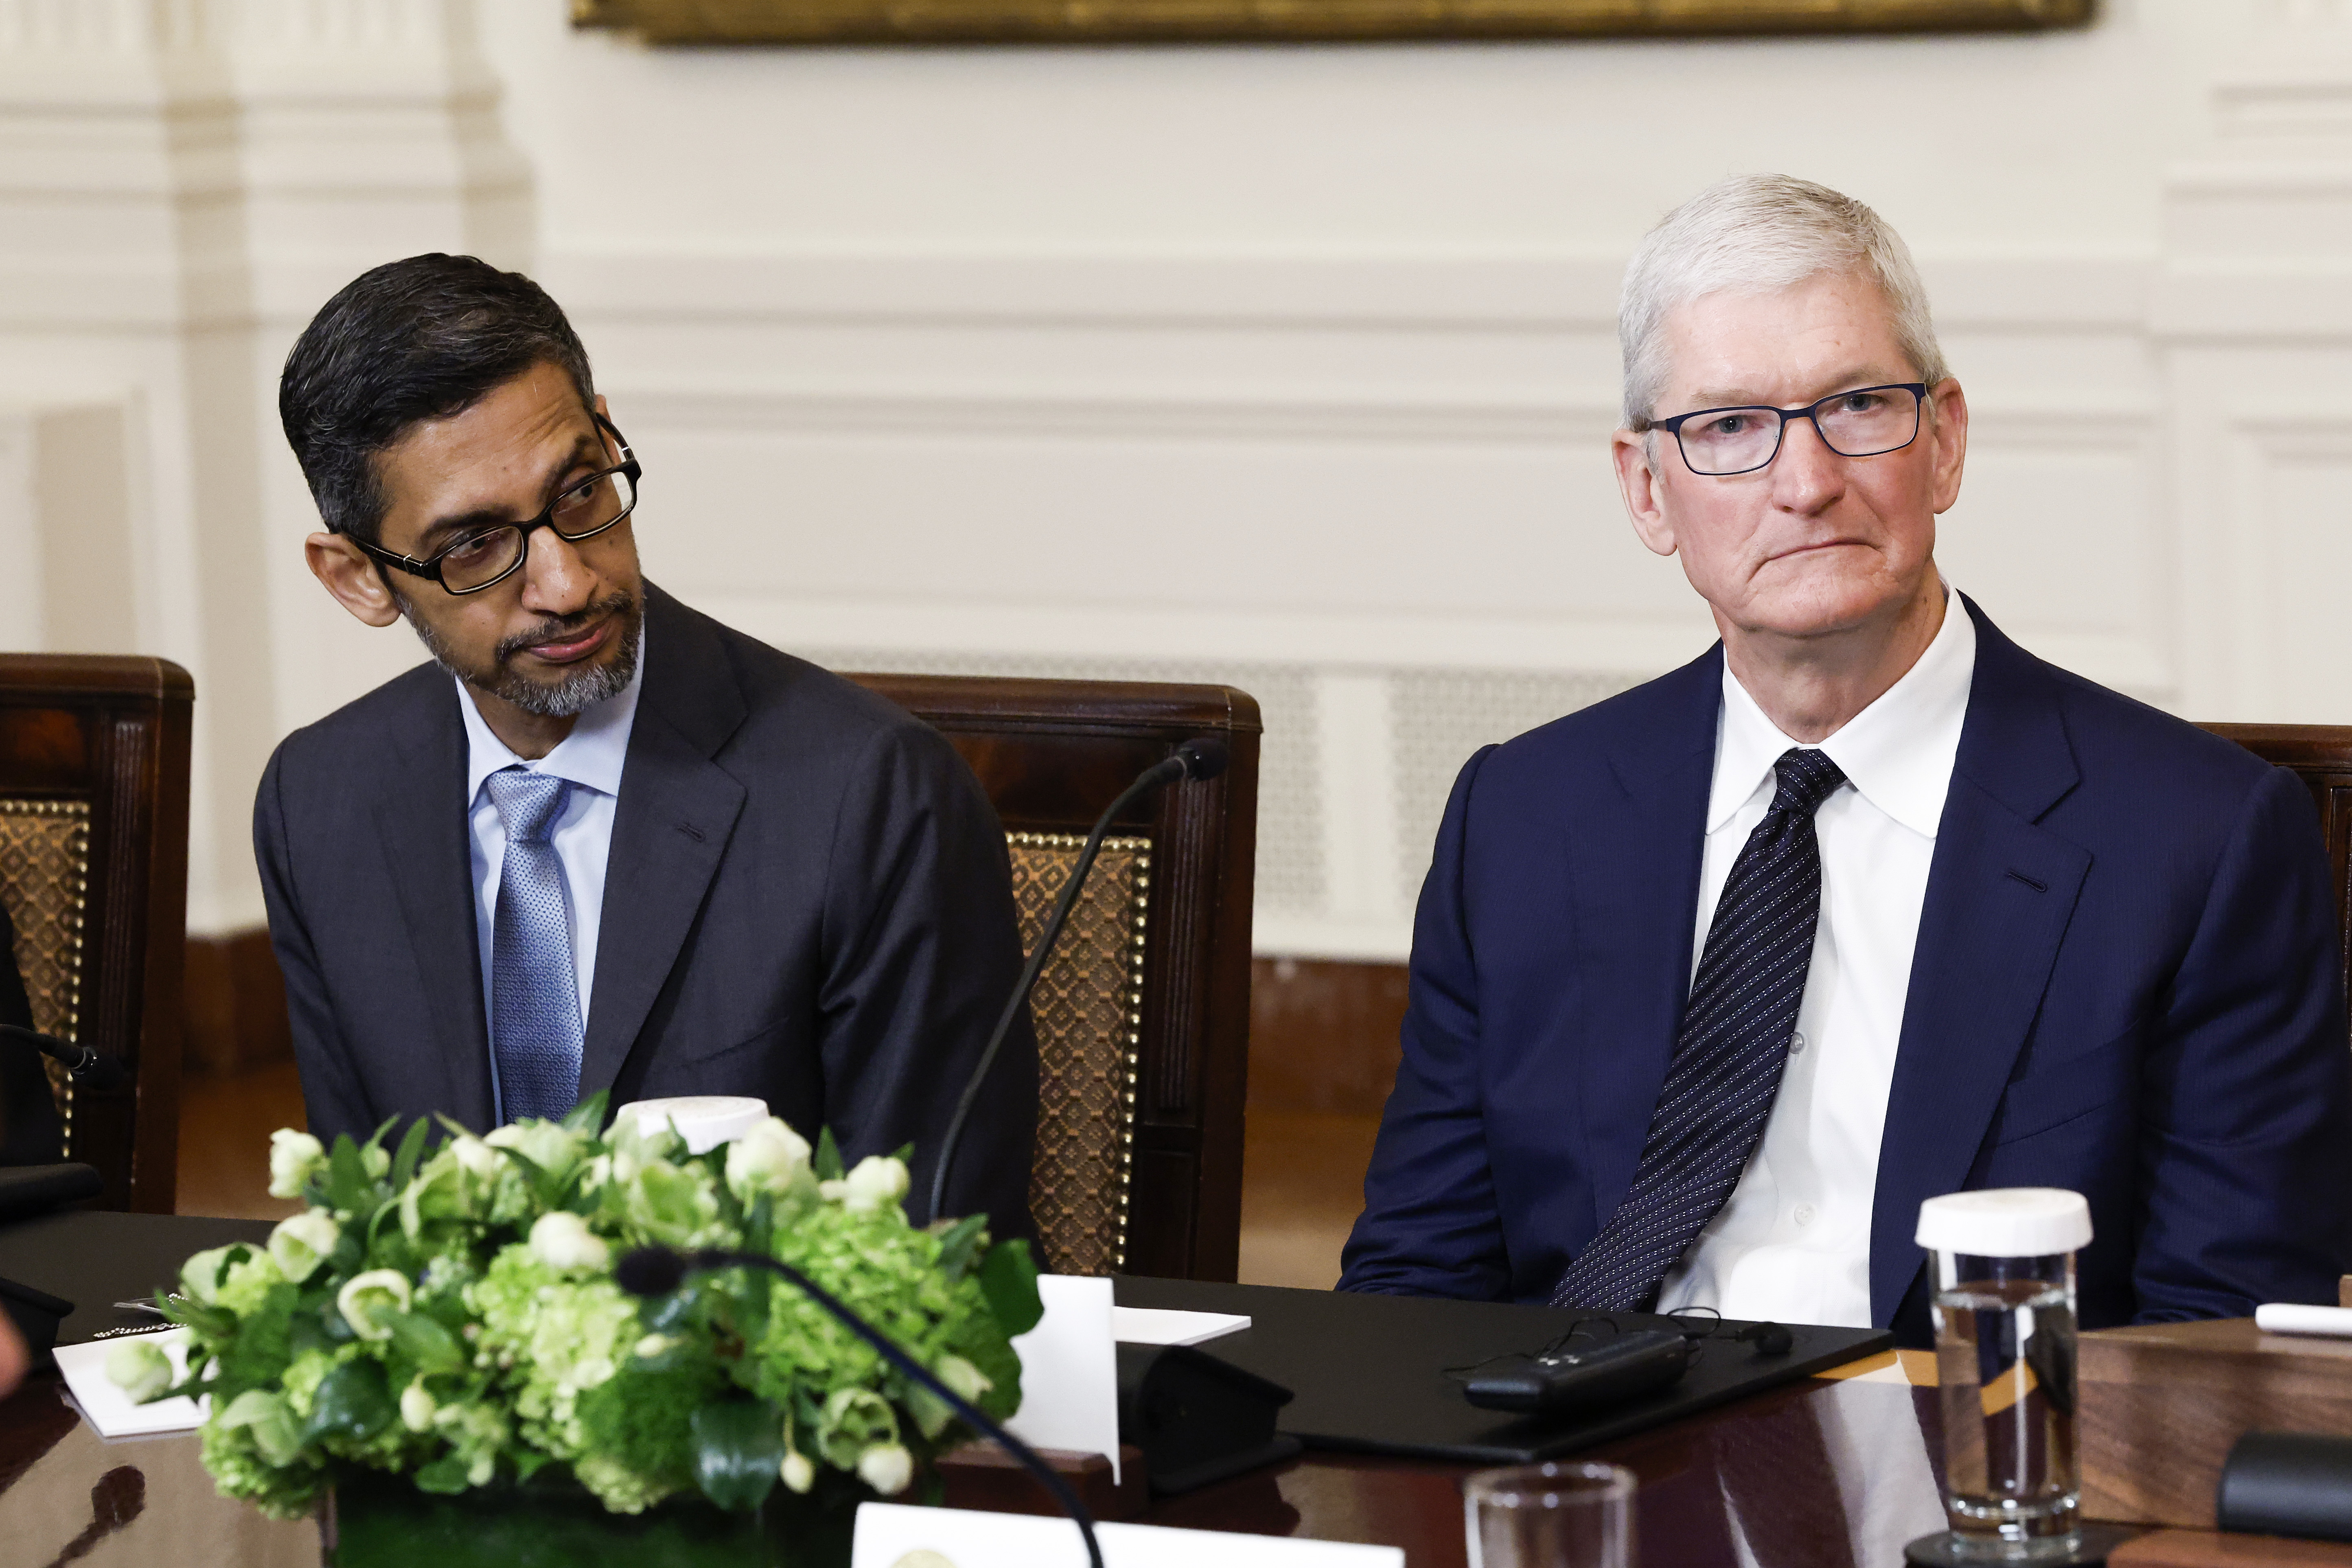
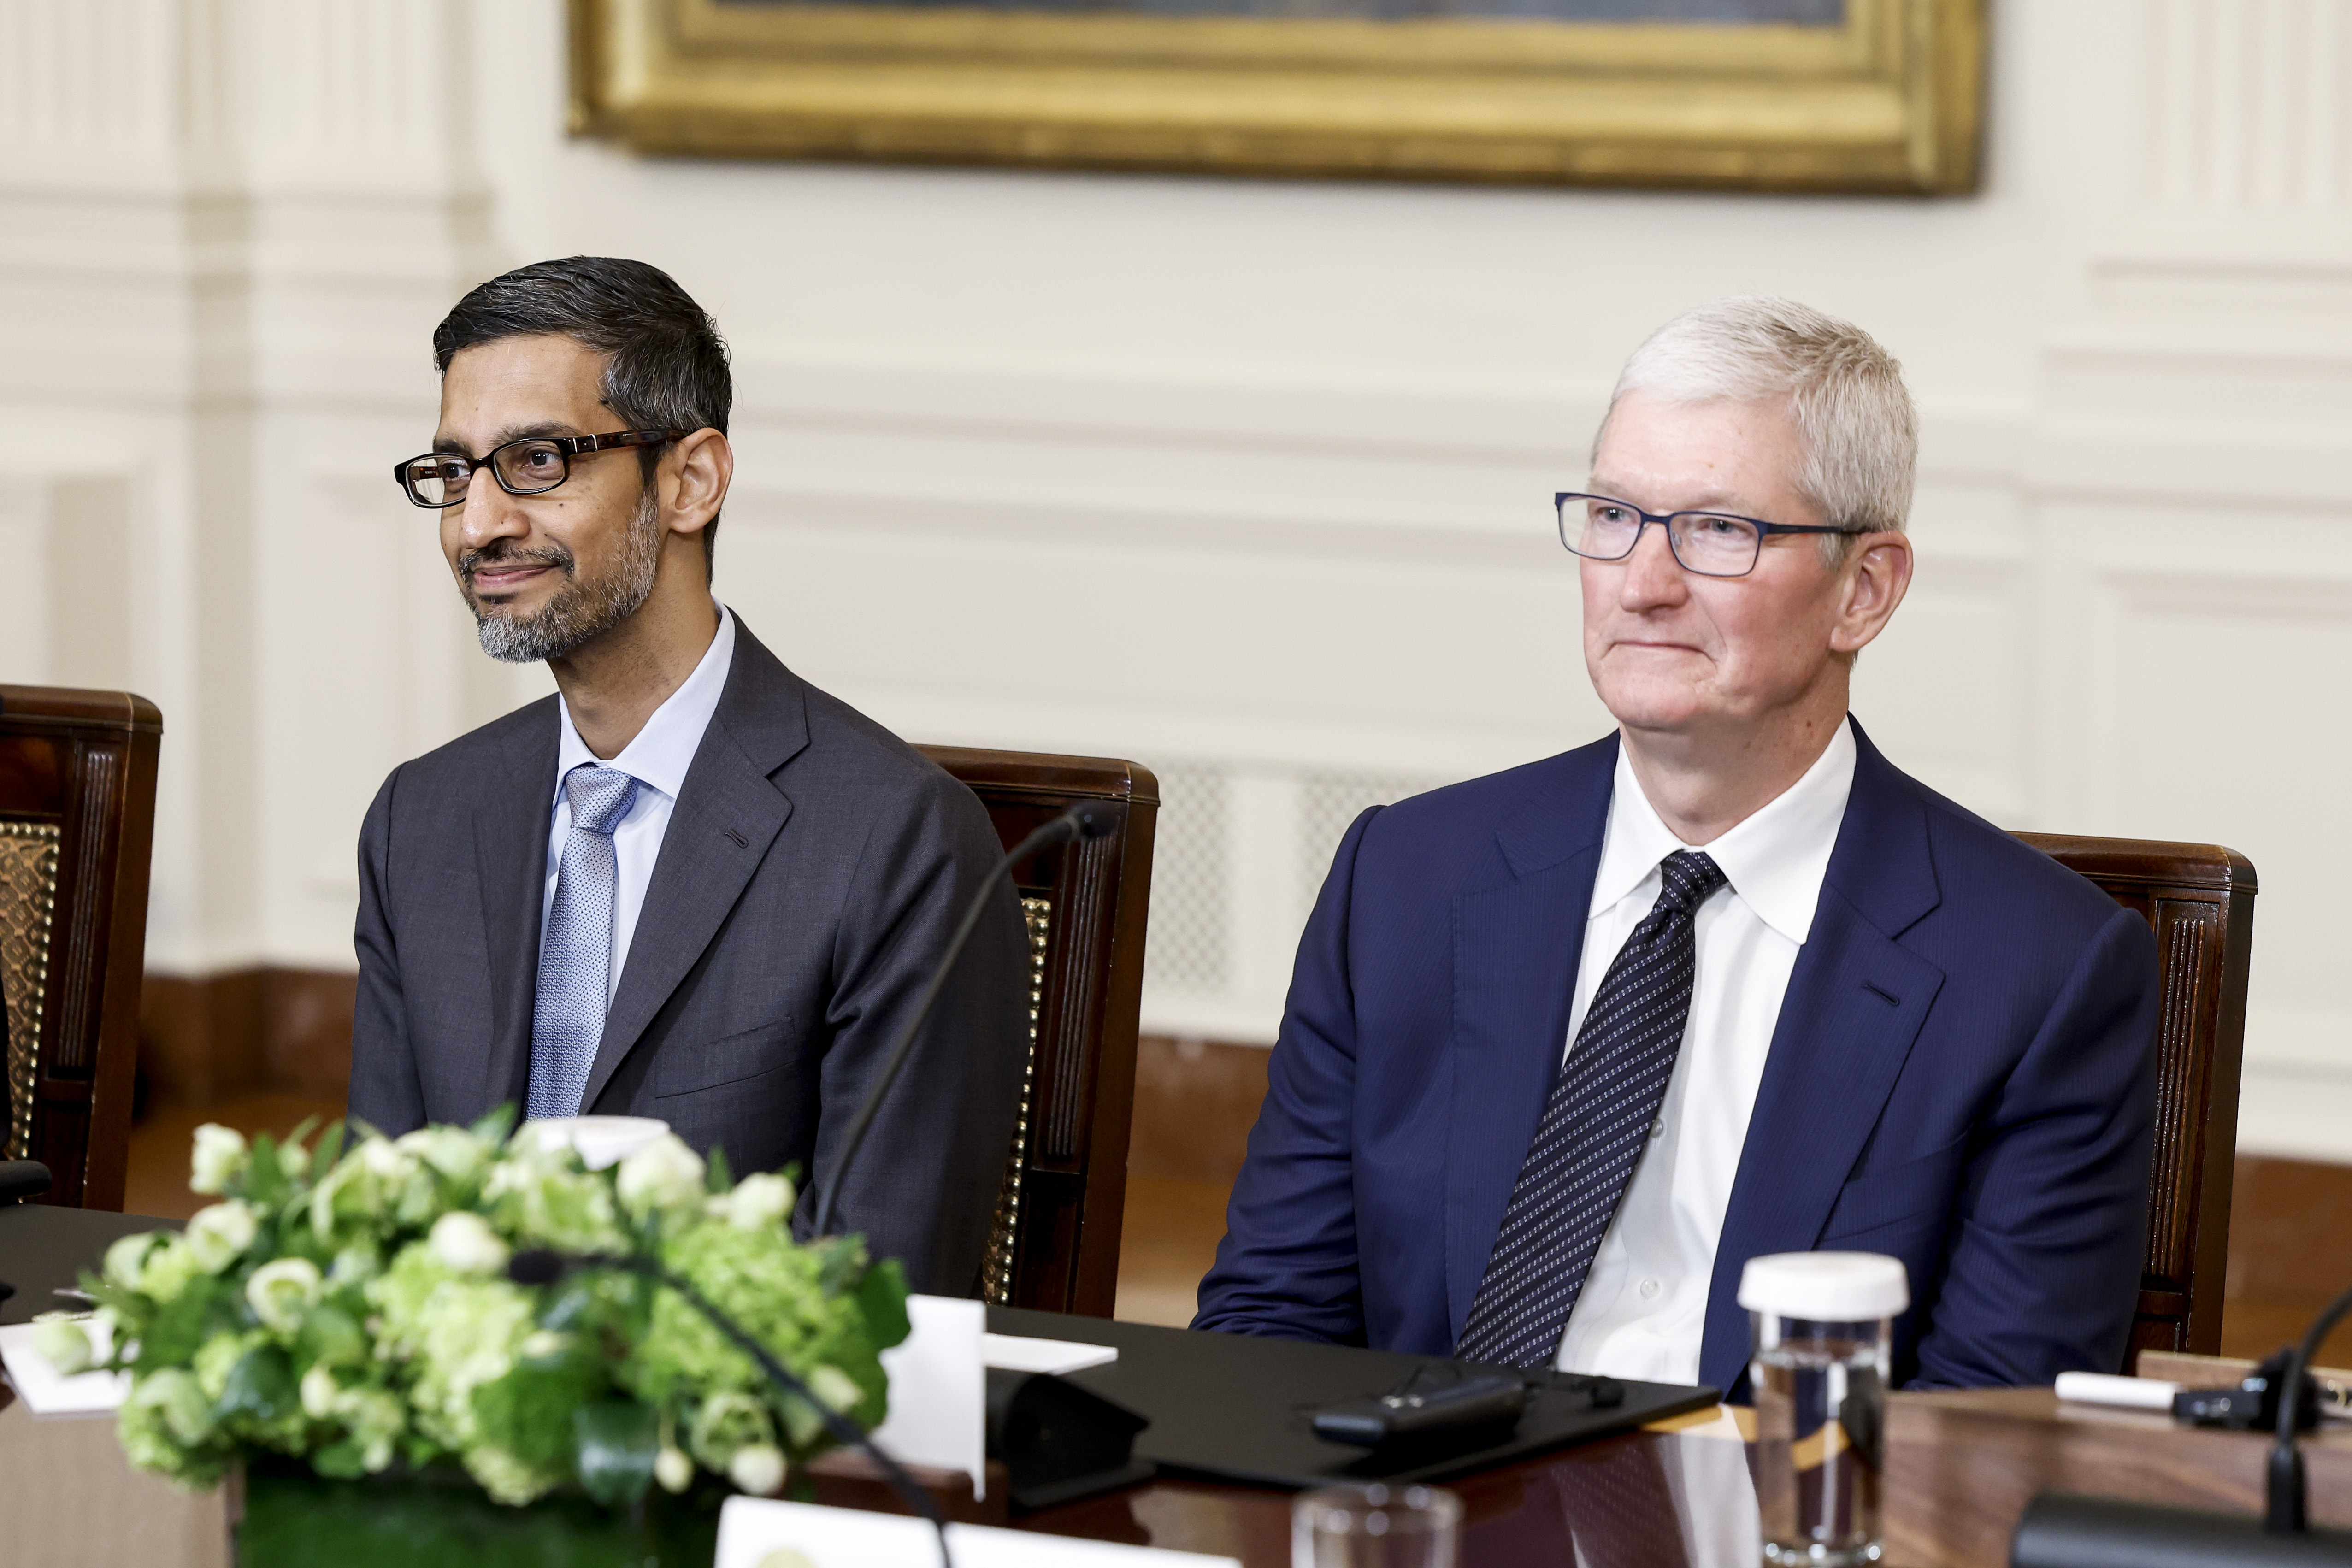
WASHINGTON, DC - JUNE 23: Google CEO Sundar Pichai (L) and Apple CEO Tim Cook (R) listen as U.S. President Joe Biden speaks during a roundtable with American and Indian business leaders in the East Room of the White House on June 23, 2023 in Washington, DC. Biden and Indian Prime Minister Narendra Modi held the meeting to meet with a range of leaders from the tech and business worlds and to discuss topics including innovation and AI. (Photo by Anna Moneymaker/Getty Images)
Anna Moneymaker via Getty Images

But that restriction only applied to X; the standalone Grok app reportedly continues to generate these images. Since Apple and Google host the apps — which their policies explicitly prohibit — you might expect them to remove them from their stores. Well, in that case, you'd be wrong.

So far, Tim Cook's Apple and Sundar Pichai's Google haven’t removed Grok from their stores — unlike similar “nudifying” apps from other developers. The companies also didn’t take any action on X while it was producing the images. That’s despite 28 women’s groups (and other progressive advocacy nonprofits) publishing an open letter calling on the companies to act.

The companies haven't replied to multiple requests for comment from Engadget. To my knowledge, they haven't acknowledged the issue publicly in any format, nor have they responded to questions from other media outlets.

Grok - App Store and Play Store listings
Apple / Google

The research’s findings on sexualized images included numerous outputs of people wearing transparent bikinis or micro-bikinis. The CCDH referred to one of a "uniformed healthcare worker with white fluids visible between her spread legs." Others included women wearing only dental floss, Saran Wrap or transparent tape. One depicted Ebba Busch, Sweden's Deputy Prime Minister, "wearing a bikini with white fluid on her head."

Other public figures were part of that group. They include Selena Gomez, Taylor Swift, Billie Eilish, Ariana Grande, Ice Spice, Nicki Minaj, Christina Hendricks, Millie Bobby Brown and Kamala Harris.

Examples of children include someone using Grok to edit a child's "before-school selfie" into an image of her in a bikini. Another image depicted "six young girls wearing micro bikinis." The CCDH said that, as of January 15, both of these posts were still live on X.

In total, 29 percent of the sexualized images of children identified in the sample were still accessible on X as of January 15. The research found that even after posts were removed, the images remained accessible via their direct URLs.

You can read the CCDH's report for more details on the results and methodology. We’ll update this story if we receive a reply from Apple or Google.

This article originally appeared on Engadget at https://www.engadget.com/ai/grok-generated-an-estimated-3-million-sexualized-images--including-23000-of-children--over-11-days-175053250.html?src=rss

1Password adds an extra layer of phishing protection

1Password has a new tool designed to counteract the advantages AI has given to phishing scammers. A new feature for the company's browser extension gives you a "second pair of eyes" to help you catch a bogus website before entering your login info.

Before AI, phishing attempts often included telltale signs like obvious typos or rudimentary graphic design. Now that AI makes it much easier to design and code convincingly, scams are on the rise. According to Fortune, 60 percent of companies reported an increase in fraud-related losses from 2024 to 2025. And the advent of AI browsers could make things even worse.

“Our new phishing feature adds an extra layer of protection,” 1Password says. Once the feature is activated, the extension actively watches for suspicious sign-ins. To be clear, even before this feature's arrival, 1Password wouldn't autofill saved credentials for a bogus website impersonating it. But that still left room for people to manually paste their login info, handing it over to those with the worst intentions.

That moment when you try to paste your login manually is where the new feature comes in. "The website you're on isn't linked to a login in 1Password," the feature's warning pop-up reads. "Make sure you trust this site before continuing."

1Password says that's the "breakthrough" moment that can help you avoid a major hassle. "That single moment of pause, that tiny bit of friction, is often all it takes to disrupt the attackers' entire plan."

The new feature is available today. You can enable it in the 1Password browser extension's settings. Under the Notifications section, activate the setting for "Warn about pasted logins on non-linked websites."

This article originally appeared on Engadget at https://www.engadget.com/cybersecurity/1password-adds-an-extra-layer-of-phishing-protection-140000293.html?src=rss

Spotify’s Prompted Playlist lets you describe exactly what you want to hear

Ahead of its upcoming price hike, Spotify is rolling out a more advanced AI playlist feature in the US and Canada. Prompted Playlist, which the company trialed in New Zealand late last year, lets subscribers "control the Spotify algorithm," as the company describes it. "You're not just asking for music, you're shaping how Spotify goes about discovering it for you."

For example, you can guide it to make a playlist of songs you've saved to your Library but haven't listened to yet. (It can tap into your entire Spotify history.) Or, you can tell it to round up songs from a specific television show or movie. (It uses real-time information about pop culture, charts, and history.)

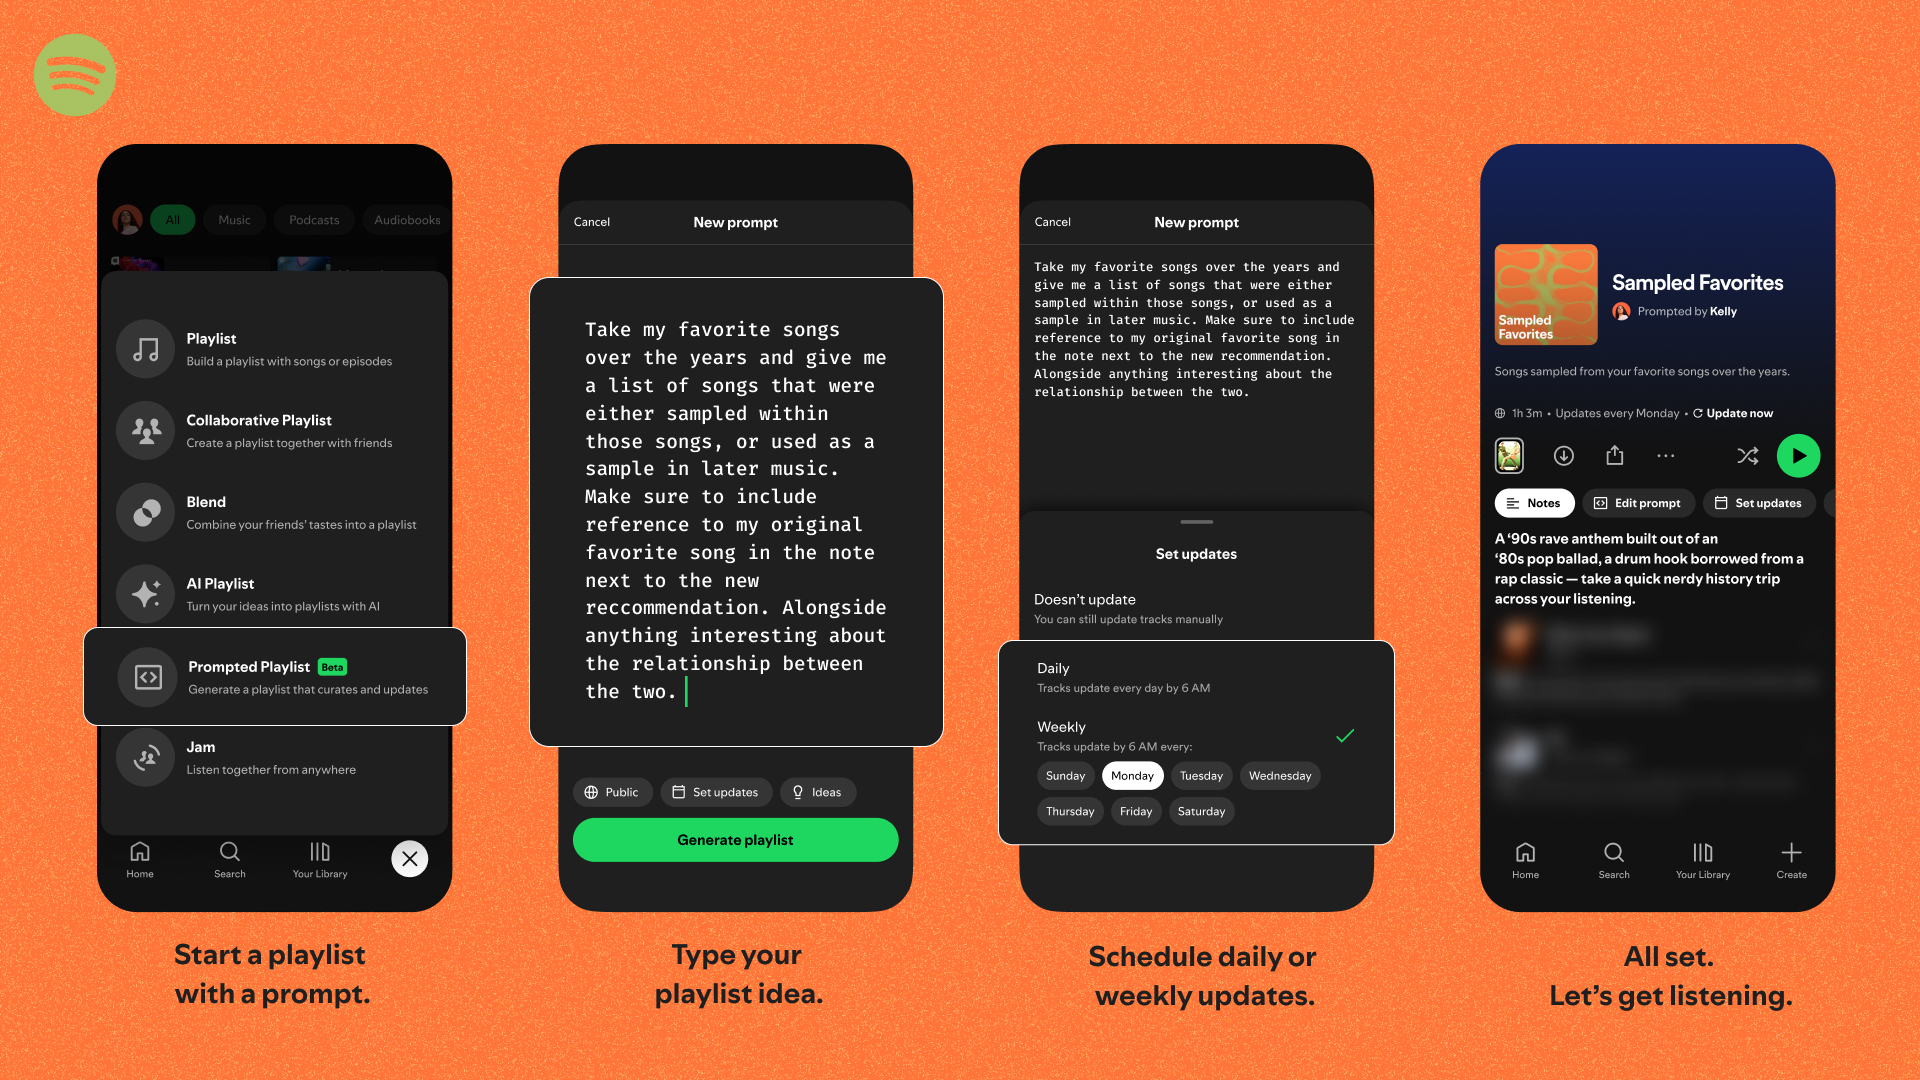
The feature includes options to refresh the playlist over time (daily or weekly). You can edit each playlist's prompt at any time. Each track will include a short note to explain why it was chosen.

Four screens showing the steps to produce a Spotify Prompted Playlist
The standard AI Playlist creator will remain alongside the new Prompted Playlist.
Spotify

Spotify says beta testers have used Prompted Playlist to revisit songs tied to specific moments and filter out tracks they've overplayed lately. "Others are asking for long, lyric-free electronic playlists to power through a workday, or mixing in artists connected to current pop culture moments and viral trends," the company wrote.

There's room for some confusion here because Spotify already has an "AI Playlist" feature. That simpler type will stick around alongside the new "Prompted" variety, which allows for finer tuning and can sift through more data.

Prompted Playlist will be available to Spotify Premium subscribers in the US and Canada "by the end of the month." Once you have access, you can try it by tapping Create, then selecting Prompted Playlist.

This article originally appeared on Engadget at https://www.engadget.com/audio/spotifys-prompted-playlist-lets-you-describe-exactly-what-you-want-to-hear-140000153.html?src=rss

Apple is reportedly developing a wearable AI pin

Apple will reportedly try to succeed where Humane failed (miserably). On Wednesday, The Information reported that the iPhone maker is working on an AI pin. The wearable is said to resemble a slightly thicker AirTag and include multiple cameras, a speaker, microphones, and wireless charging.

The report coincides with another from Bloomberg that claims that Apple will revamp Siri as a ChatGPT-style chatbot. When combined with the recent announcement that Google's Gemini will power Siri AI, it looks like the company is finally making a more defined play for a piece of the generative AI pie. On the other hand, the wearable pin is reportedly only in the very early stages and could still be canceled.

The pin is described as a thin, flat, circular disc with an aluminum and glass exterior. It includes two cameras (standard and wide-angle) for taking photos and videos of the user's surroundings. It also has three microphones. It includes a speaker and a physical button along one edge. It has a magnetic inductive charging interface, similar to the Apple Watch's charging mechanism.

Given the way Apple markets itself as a privacy-focused company, it will be interesting to see how the company pitches the public on what sounds like an incognito recording device. Although on that note, the App Store still hosts the Grok app, which egregiously violates privacy by generating nearly-nude deepfakes of real people — despite Apple's rules explicitly prohibiting such apps.

The Information says Apple could release its AI pin as early as 2027. The company sounds confident in the device's appeal, as it reportedly plans to produce around 20 million units at launch.

This article originally appeared on Engadget at https://www.engadget.com/wearables/apple-is-reportedly-developing-a-wearable-ai-pin-204705065.html?src=rss

Meta is expanding Threads ads to all users globally

Threads has grown enough for Meta to fully integrate it into its advertising machine. On Wednesday, the company said that, with the platform now hosting 400 million monthly active users, ads are expanding globally to all users. The inevitable move follows a test in 30 countries early last year.

Ads on Threads are powered by Meta's AI-powered advertising system. They'll use the "same level of personalization" (i.e., tracking and profiling) as Facebook and Instagram. Image, video and carousel ad formats will all appear natively in Threads feeds.

Meta said the ad expansion will begin next week, but the full rollout will take months. "Ads on Threads expansion to all users will be gradual, with ad delivery initially remaining low as we reach global user availability in the coming months," the company wrote in a blog post.

This article originally appeared on Engadget at https://www.engadget.com/social-media/meta-is-expanding-threads-ads-to-all-users-globally-183900226.html?src=rss

Earth is having some issues, so let’s enjoy the Webb telescope’s new nebula image

Sometimes, you just need to give your mind a little vacation. And these days, outer space sounds like as good a destination as any. Thankfully, the James Webb Space Telescope (JWST) is here to give us a dazzling new image of the Helix Nebula.

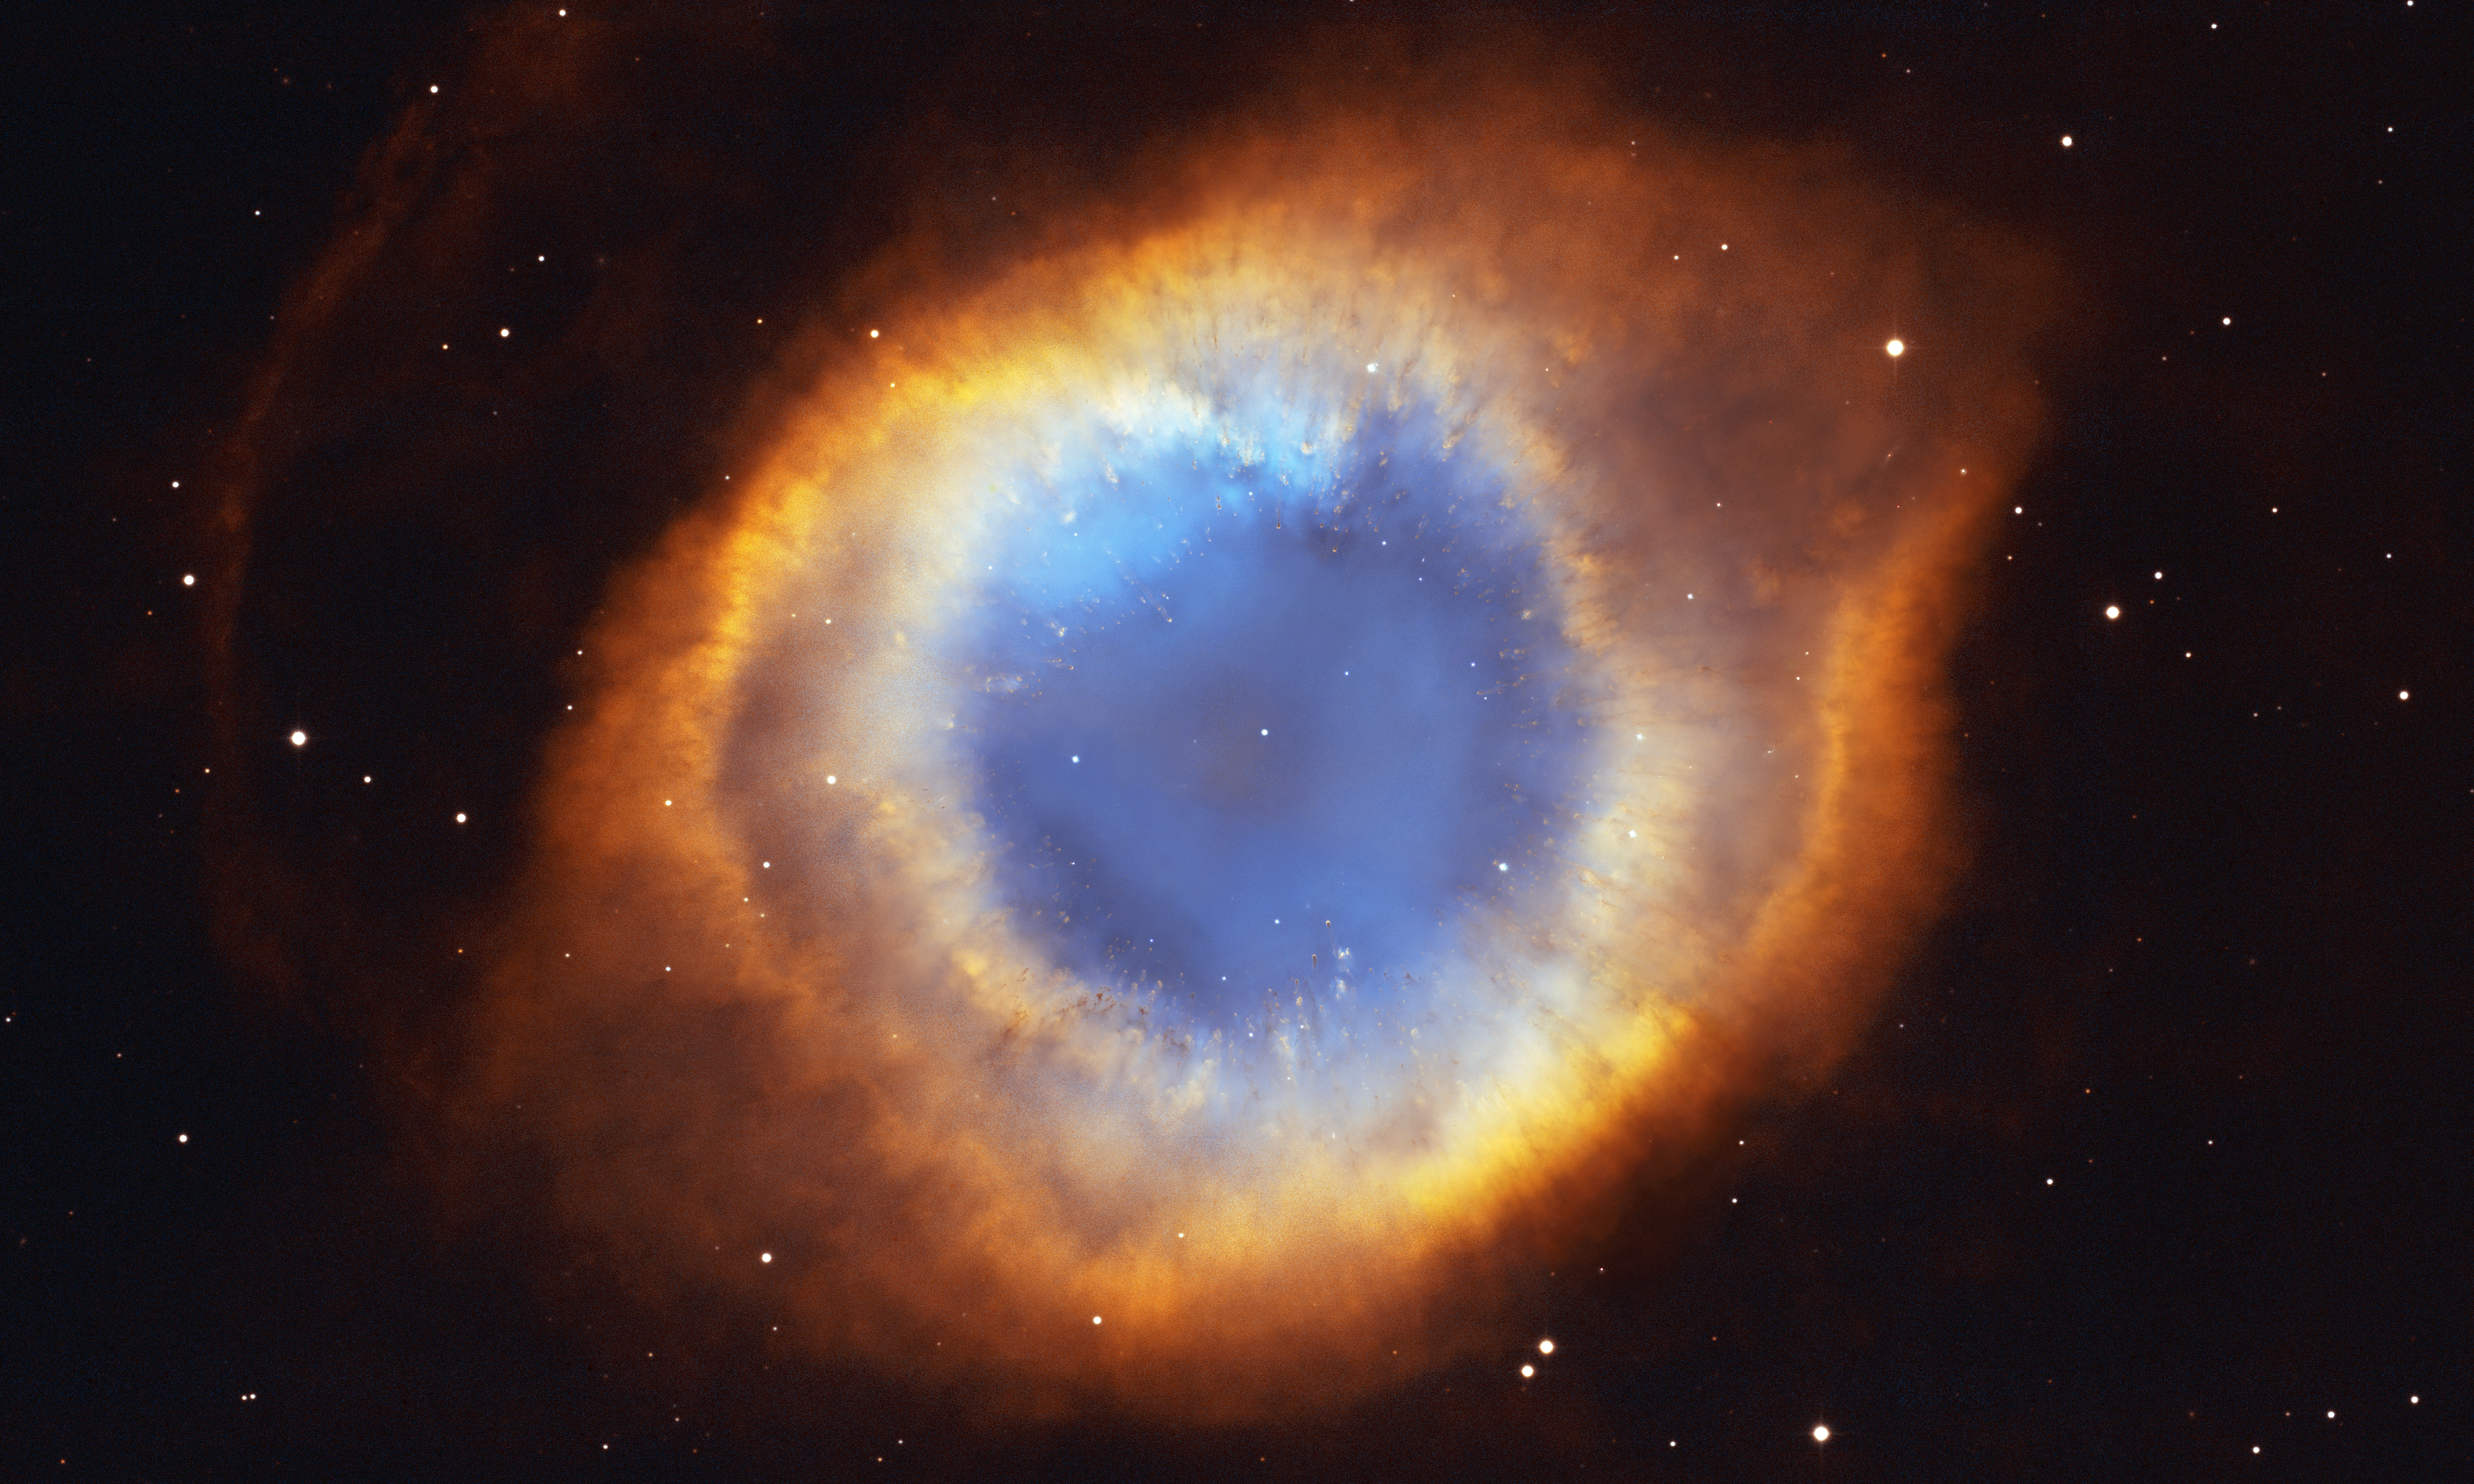
Discovered in the early 19th century, the Helix Nebula resides in the constellation Aquarius. (Cue The 5th Dimension.) At about 655 light-years away, it's one of Earth's closest planetary nebulae. When zoomed farther out, it's easy to see why it's been nicknamed the Eye of God or Eye of Sauron. This 2004 image from the Hubble telescope illustrates that.

An eye-like nebula in space
A wider view of the same nebula from 2004
NASA / ESA / C.R. O'Dell (Vanderbilt University) / M. Meixner / P. McCullough / G. Bacon ( STSI)

What we're seeing in the nebula is, in a sense, a moment of death that lays the groundwork for a new birth. The dying star (out of frame in the closer new image) sheds its outer layers. As expelled gas and dust cool, they provide raw material that could someday form new stars and perhaps planetary systems.

The new image from Webb's NIRCam (Near-Infrared Camera) provides a much closer, higher-resolution view.

Pillar-like reddish knots in the Helix Nebula

Those pillars you see are called cometary knots, and this image is our best view of those to date. "Here, blistering winds of hot gas from the dying star are crashing into colder shells of dust and gas that were shed earlier in its life, sculpting the nebula's remarkable structure," the ESA wrote in its press release.

The knots' colors represent temperature and chemistry. Hints of blue indicate the hottest gas (energized by ultraviolet light). The yellow regions, where hydrogen atoms form molecules, are farther from the nebula's nucleus (and therefore cooler). On the edges, reddish-orange regions depict the coolest material, where gas thins and dust begins to form.

This article originally appeared on Engadget at https://www.engadget.com/science/space/earth-is-having-some-issues-so-lets-enjoy-the-webb-telescopes-new-nebula-image-181049901.html?src=rss

The mother of one of Elon Musk’s children is suing xAI over nonconsensual deepfake images

Although X removed Grok’s ability to create nonconsensual digitally undressed images on the social platform, the standalone Grok app is another story. It reportedly continues to produce “nudified” deepfakes of real people. And now, Ashley St. Clair, a conservative political strategist and mother of one of Elon Musk’s 14 children, has sued xAI for nonconsensual sexualized images of her that Grok allegedly produced.

In the court filing, St. Clair accused xAI’s Grok chatbot of creating and disseminating deepfakes of her “as a child stripped down to a string bikini, and as an adult in sexually explicit poses, covered in semen, or wearing only bikini floss.” In some cases, the chatbot allegedly produced bikini-clad deepfakes of St. Clair based on a photo of her as a 14-year-old. “People took pictures of me as a child and undressed me. There’s one where they undressed me and bent me over, and in the background is my child’s backpack that he’s wearing right now,” she said.

“I am also seeing images where they add bruises to women, beat them up, tie them up, mutilated,” St. Clair told The Guardian. “These sickos used to have to go to the dark depths of the internet, and now it is on a mainstream social media app.”

St. Clair said that, after she reported the images to X, the social platform replied that the content didn’t violate any policies. In addition, she claims that X left the images posted for up to seven days after she reported them. St. Clair said xAI then retaliated against her by creating more digitally undressed deepfakes of her, therefore “making [St. Clair] the laughingstock of the social media platform.”

She accused the company of then revoking her X Premium subscription, verification checkmark and ability to monetize content on the platform. “xAI further banned [her] from repurchasing Premium,” St. Clair’s court filing states.

On Wednesday, X said it changed its policies so that Grok would no longer generate sexualized images of children or nonconsensual nudity “in those jurisdictions where it’s illegal.” However, the standalone Grok app reportedly continues to undress and sexualize photos when prompted to do so.

WASHINGTON, DC - JUNE 23: Google CEO Sundar Pichai (L) and Apple CEO Tim Cook (R) listen as U.S. President Joe Biden speaks during a roundtable with American and Indian business leaders in the East Room of the White House on June 23, 2023 in Washington, DC. Biden and Indian Prime Minister Narendra Modi held the meeting to meet with a range of leaders from the tech and business worlds and to discuss topics including innovation and AI. (Photo by Anna Moneymaker/Getty Images)
Neither Apple nor Google has removed the Grok app despite explicit policy violations.
Anna Moneymaker via Getty Images

Apple and Google have thus far done, well, absolutely nothing. Despite the multi-week outrage over the deepfakes — and an open letter from 28 advocacy groups — neither company has removed the X or Grok apps from their app stores. Both the App Store and Play Store have policies that explicitly prohibit apps that generate such content.

Neither Apple nor Google has responded to multiple requests for comment from Engadget. That includes a follow-up email sent on Friday, regarding the Grok app continuing to “nudify” photos of real women and other people.

While Apple and Google fail to act, many governments have done the opposite. On Monday, Malaysia and Indonesia banned Grok. The same day, UK regulator Ofcom opened a formal investigation into X. California opened one on Wednesday. The US Senate even passed the Defiance Act for a second time in the wake of the blowback.

“If you are a woman, you can’t post a picture, and you can’t speak, or you risk this abuse,” St. Clair told The Guardian. “It’s dangerous, and I believe this is by design. You are supposed to feed AI humanity and thoughts, and when you are doing things that particularly impact women, and they don’t want to participate in it because they are being targeted, it means the AI is inherently going to be biased.”

Speaking about Musk and his team, she added that “these people believe they are above the law, because they are. They don’t think they are going to get in trouble, they think they have no consequences.”

This article originally appeared on Engadget at https://www.engadget.com/ai/the-mother-of-one-of-elon-musks-children-is-suing-xai-over-nonconsensual-deepfake-images-191451979.html?src=rss

TikTok sued by former workers over alleged union-busting

You know things are messed up when a Big Tech company fights accusations of union-busting by insisting it was only AI layoffs. That's where things stand after a group of fired TikTok moderators in the UK filed a legal claim with an employment tribunal. The Guardian reported on Friday that around 400 TikTok content moderators who were unionizing were laid off before Christmas.

The workers were sacked a week before a vote was scheduled to establish a collective bargaining unit. The moderators said they wanted better protection against the personal toll of processing traumatic content at a high speed. They accused TikTok of unfair dismissal and violating UK trade union laws.

"Content moderators have the most dangerous job on the internet," John Chadfield, the national officer for tech workers at the Communication Workers Union (CWU), said in a statement to The Guardian. "They are exposed to the child sex abuse material, executions, war and drug use. Their job is to make sure this content doesn't reach TikTok's 30 million monthly users. It is high pressure and low paid. They wanted input into their workflows and more say over how they kept the platform safe. They said they were being asked to do too much with too few resources."

TikTok denied that the firings were union-busting, calling the accusations "baseless." Instead, the company claimed the layoffs were part of a restructuring plan amid its adoption of AI for content moderation. The company said 91 percent of transgressive content is now removed automatically.

The company first announced a restructuring exercise in August, just as hundreds of moderators in TikTok's London offices were organizing for union recognition. At the time, John Chadfield, CWU's National Officer for Tech, said the workers had long been "sounding the alarm over the real-world costs of cutting human moderation teams in favour of hastily developed, immature AI alternatives."

"That TikTok management have announced these cuts just as the company's workers are about to vote on having their union recognised stinks of union-busting and putting corporate greed over the safety of workers and the public,” Chadfield said.

This article originally appeared on Engadget at https://www.engadget.com/big-tech/tiktok-sued-by-former-workers-over-alleged-union-busting-170446921.html?src=rss

Flaw in 17 Google Fast Pair audio devices could let hackers eavesdrop

Now would be a good time to update all your Bluetooth audio devices. On Thursday, Wired reported on a security flaw in 17 headphone and speaker models that could allow hackers to access your devices, including their microphones. The vulnerability stems from a faulty implementation of Google's one-tap (Fast Pair) protocol.

Security researchers at Belgium's KU Leuven University Computer Security and Industrial Cryptography group, who discovered the security hole, named the flaw WhisperPair. They say a hacker within Bluetooth range would only require the accessory's (easily attainable) device model number and a few seconds.

"You're walking down the street with your headphones on, you're listening to some music. In less than 15 seconds, we can hijack your device," KU Leuven researcher Sayon Duttagupta told Wired. "Which means that I can turn on the microphone and listen to your ambient sound. I can inject audio. I can track your location." The researchers notified Google about WhisperPair in August, and the company has been working with them since then.

Fast Pair is supposed to only allow new connections while the audio device is in pairing mode. (A proper implementation of this would have prevented this flaw.) But a Google spokesperson told Engadget that the vulnerability stemmed from an improper implementation of Fast Pair by some of its hardware partners. This could then allow a hacker's device to pair with your headphones or speaker after it's already paired with your device.

"We appreciate collaborating with security researchers through our Vulnerability Rewards Program, which helps keep our users safe," a Google spokesperson wrote in a statement sent to Engadget. "We worked with these researchers to fix these vulnerabilities, and we have not seen evidence of any exploitation outside of this report's lab setting. As a best security practice, we recommend users check their headphones for the latest firmware updates. We are constantly evaluating and enhancing Fast Pair and Find Hub security."

The researchers created the video below to demonstrate how the flaw works

In an email to Engadget, Google said the steps required to access the device’s microphone or audio are complex and involve multiple stages. The attackers would also need to remain within Bluetooth range. The company added that it provided its OEM partners with recommended fixes in September. Google also updated its Validator certification tool and its certification requirements.

The researchers say that, in some cases, the risk applies even to those who don't use Android phones. For example, if the audio accessory has never been paired with a Google account, a hacker could use WhisperPair to not only pair with the audio device but also link it to their own Google account. They could then use Google's Find Hub tool to track the device's (and therefore your) location.

Google said it rolled out a fix to its Find Hub network to address that particular scenario. However, the researchers told Wired that, within hours of the patch’s rollout, they found a workaround.

The 17 affected devices are made by 10 different companies, all of which received Google Fast Pair certification. They include Sony, Jabra, JBL, Marshall, Xiaomi, Nothing, OnePlus, Soundcore, Logitech and Google. (Google says its affected Pixel Buds are already patched and protected.) The researchers posted a search tool that lets you see if your audio accessories are vulnerable.

In a statement sent to Engadget, OnePlus said it's investigating the issue and "will take appropriate action to protect our users' security and privacy." Marshall said it patched the issue in November and is working with Google to avoid similar issues in the future (see full statement below). We also contacted the other accessory makers and will update this story if we hear back.

The researchers recommend updating your audio devices regularly. However, one of their concerns is that many people will never install the third-party manufacturer's app (required for updates), leaving their devices vulnerable.

The full report from Wired has much more detail and is worth a read.

Update, January 15 2026, 4:04PM ET: “We can confirm that Marshall has issued the necessary firmware updates and security patches to address the headphones potentially affected,” a company representative told Engadget. “These updates have been available since November and have been offered to all users since then. While this is an industry-wide issue, we take it seriously and are working closely with Google to reduce the risk of similar vulnerabilities in the future.”

This article originally appeared on Engadget at https://www.engadget.com/cybersecurity/flaw-in-17-google-fast-pair-audio-devices-could-let-hackers-eavesdrop-194613456.html?src=rss